Fortify
A defensive, quick-deploy protection layer for Tor hidden services — disposable entry points, a proof-of-work gate, and progressive trust, all in Rust with no client-side JavaScript.
The core principle
Everything in Fortify exists to preserve one rule: the real hidden service is never directly exposed, never public, and never connected to by any public-facing address.
It's a defensive system only. Availability is treated as secondary to secrecy, and every component is designed to degrade safely rather than fail open.
Address topology
Instead of a single public entry point, Fortify generates multiple public orchestrators — functionally identical mirrors that reverse-proxy traffic, load balance across nodes, and classify sessions. Critically, none of them ever connect to the real hidden service.
Why mirrors are worth the complexity:
- Onion addresses do get burned under sustained attack.
- Tor circuits can degrade or stall.
- Attackers frequently pin traffic to a single known onion.
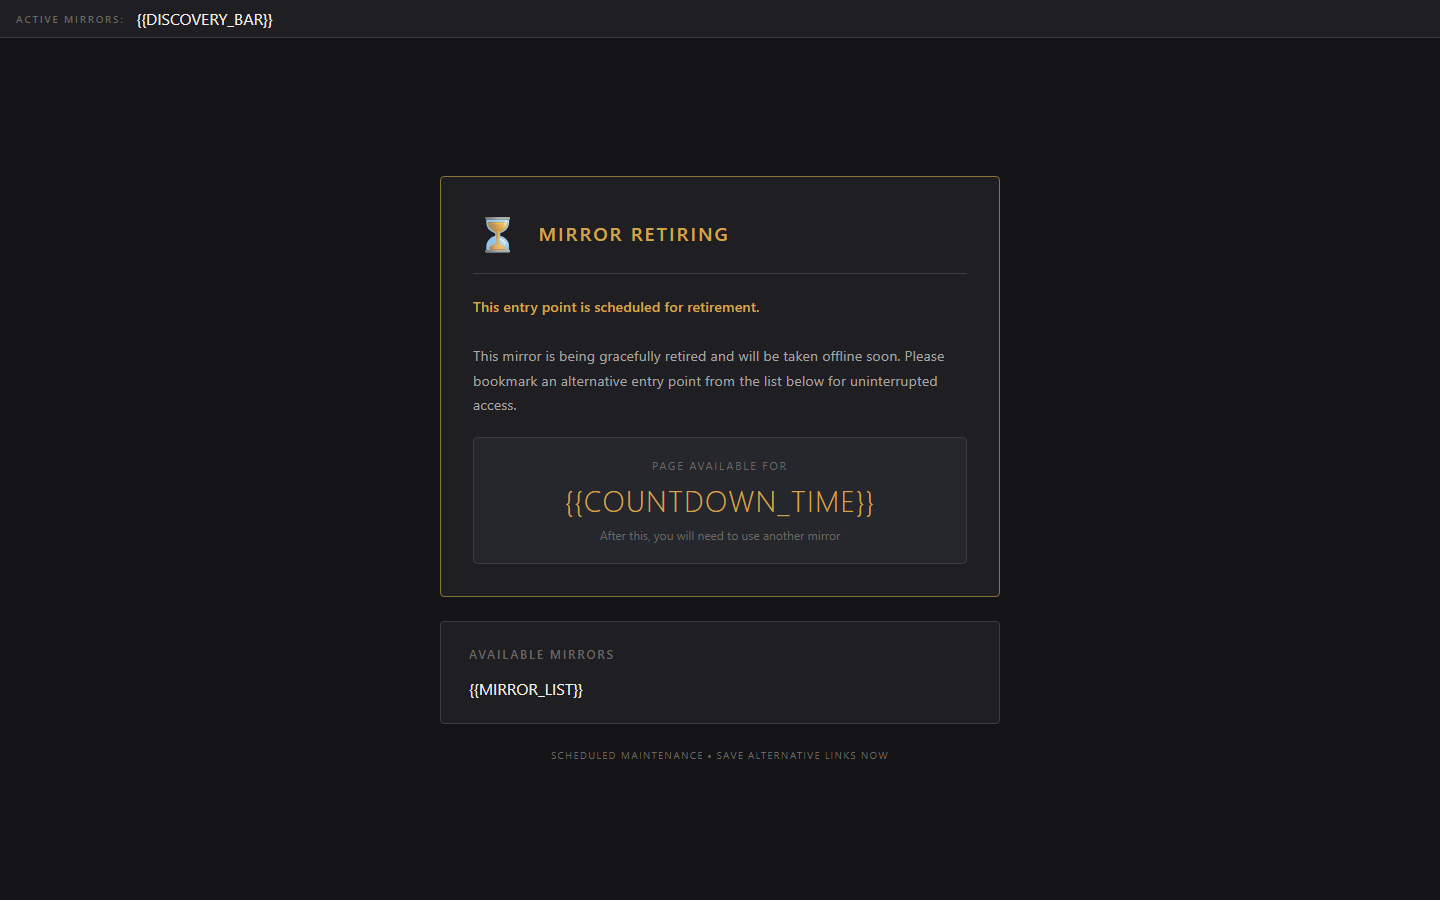
Rotatable entry points materially improve survivability. When a mirror becomes overloaded, targeted by sustained abuse, or functionally degraded, Fortify may mark it "burned": gracefully drain or hard-drop its traffic, spawn a replacement mirror, and update internal routing tables.
Users arriving at a burned mirror see a hard captcha challenge and a message that the mirror is no longer valid. A successful captcha migrates the session to a healthy orchestrator and issues a new mirror address for that session — which deliberately prevents automated migration and forces human verification at the exact moment it matters most.
Traffic classification
Every session falls into one of three classes, and the class determines which pool handles it:
| Class | Routed to | Behavior |
|---|---|---|
| Unknown / first-time | Threat nodes | Captcha on every page load, no long-lived trust, promotion only after successful challenges |
| Verified / healthy | Healthy nodes | Fast path — minimal inspection, pre-approved routing, direct proxy |
| Degraded / suspicious | Threat nodes | Reclassified silently, tracked, and re-promoted only on evidence of good behavior |
Only healthy nodes forward traffic to the real hidden service. That single constraint is what makes the whole architecture work — the real address is reachable only through nodes that already trust you.
The gate — where Fortify is allowed to be slow
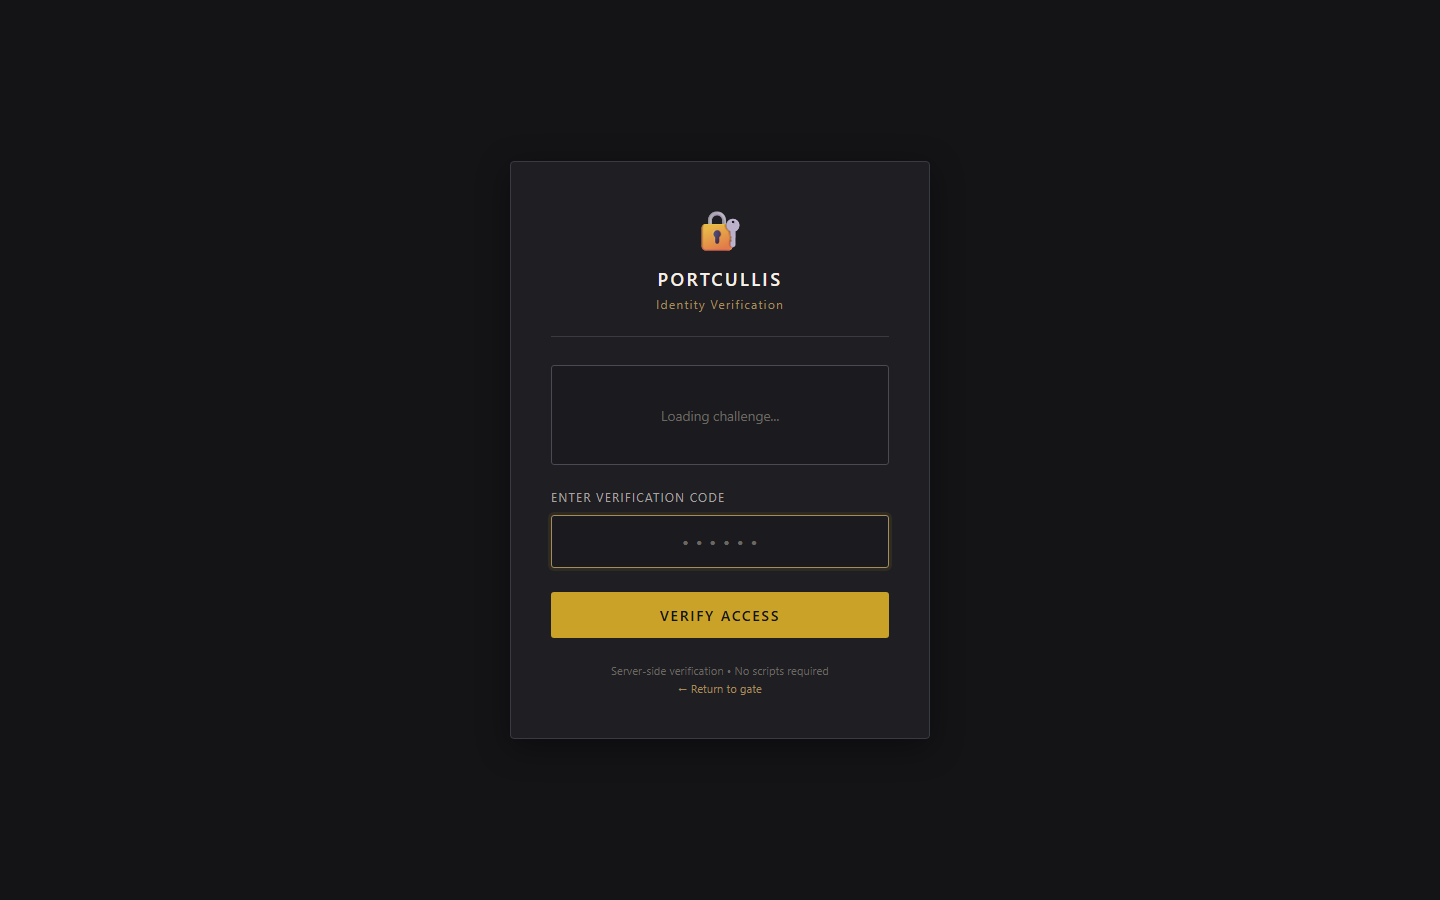
The initial gate is the primary defense wall, and it's intentionally expensive. Two mechanisms run there:
- Proof of work — a server-issued SHA-256 challenge with difficulty that adapts to current load.
- Hard-mode captcha — image or logic based, regenerated on every failure, never reused. No audio fallback, because that's the reality on Tor.
Deliberate delay is used as a weapon: humans tolerate it, automated clients suffer under it.
This is a hard constraint, not a preference. Every check happens server-side using pure HTML and HTTP challenge/response. Client-side JavaScript would mean a scriptable verification surface, which defeats the purpose of a gate.
The fast path
Once verified, the user should never pay for the gate again. The post-verification path deliberately has no proof of work, no captcha, and no artificial delays: minimal request inspection, pre-approved routing, and cached policy decisions.
Legitimate users are never punished unless their behavior proves hostile. A defense layer that makes its own users suffer is a defense layer they'll route around.
Trust model
Sessions move through a five-tier trust system from Burned to Trusted, with a session state machine handling promotion and demotion, violation tracking, and burn logic. Trust is granted by a short-lived, HMAC-SHA256-signed token that maps to a trust tier and a node pool.
A token never grants permanent trust — promotion is progressive, and a session can be demoted silently based on the behavioral signals its node observes.
Node system
Nodes operate in two modes, each with adaptive rate limiting:
- Healthy nodes — forward requests to the real backend service.
- Threat nodes — handle unverified traffic and enforce the gate.
Both modes run violation detection (rate limits, suspicious patterns, invalid paths) and behavioral anomaly detection. Violations feed the trust state machine, so a node's job isn't just to serve traffic — it's to decide what that traffic has earned.
Routing strategies
The proxy layer supports three strategies — round-robin, least-connections, and weighted-random — plus tier-based routing that sends healthy and threat traffic to separate pools. Backpressure and request caps prevent the system from accepting more work than it can handle.
That last part matters: excess traffic is throttled, not accepted. Onion services have finite hardware, and a protection layer that accepts more load than the hardware can carry isn't protecting anything.
Scaling model
Scaling is adaptive and explicitly capped. Node ratios are configurable — a typical split might be 70% healthy, 30% threat — with a hard cap at roughly 75% system resource utilization.
| Traffic target | Healthy nodes | Threat nodes |
|---|---|---|
| ~1,000 visits/day | 5 | 2 |
| ~5,000 visits/day | 10 | 4 |
| ~25,000 visits/day | 50 | 10 |
Those numbers are illustrative rather than fixed, but the principle isn't: the system refuses to improve throughput by compromising safety.
Host hardening
Fortify's hardening runs before Tor services start. It detects its environment — bare metal vs. VM vs. container, disk type, CPU and RAM ceilings — and adjusts its hardening profile to match.
- Services and SSH — unused services disabled, SSH locked to key-only auth, rate-limited, optionally on a non-standard port.
- sysctl — TCP SYN protections, ICMP rate limiting, file-descriptor limits.
- Mount options — noexec, nosuid, and nodev where applicable.
- Visibility — restricted /proc, /sys, and /dev.
- cgroups — limits to prevent fork bombs and memory exhaustion.
Damage containment
Each component runs as a separate user with separate permissions. No component keeps root after install, and no component can reach another's secrets. The compromise of one node is not the compromise of the system.
Tor-level configuration
- Hidden service isolation — separate Tor instances (or identities) for public orchestrators, healthy nodes, and threat nodes, with separate keys, separate data directories, and no shared circuits between classes.
- Circuit hygiene — short-lived circuits for threat nodes, longer-lived for healthy sessions, with aggressive renewal on suspicious behavior.
- Connection limits — per-onion connection caps and bandwidth ceilings that hard-drop under overload, failing closed rather than open.
Optional community discovery
Fortify can optionally participate in a daisy-chained, decentralized discovery network with no central authority. Each discoverable instance may expose one or more seed addresses; joining one member's network discovers the entire connected network.
Networks are transitive — if A trusts B and B trusts C, then A, B, and C share a network. Every member hosts the same community listing of member onion addresses (public entry points only) with optional operator-defined metadata.
I'm honest about the trade-off here: this is powerful and it's risky. Discovery grows fast, and one bad actor pollutes the graph. So it ships with hard boundaries:
- Community participation is never default — it's explicit opt-in, and irreversible once joined by design.
- Community traffic never bypasses Fortify's protections.
- Real hidden service addresses are never shared, even internally.
- The network registry is signed and verified to prevent poisoning.
For v1 this is framed as experimental and opt-in. Trust scoring, revocation, and segmentation are the obvious next steps, and I'd rather name them than pretend the first version solves them.
Engineering choices
Rust was chosen deliberately, and the reasoning was ordered before the decision: security first, then deterministic performance, then minimal runtime complexity, then auditability.
- Memory safety by default — no use-after-free, no buffer overflows, which matters enormously when you're parsing untrusted input continuously.
- Static binaries — easy deployment, minimal runtime dependencies.
- Strong types — fewer logic bugs in security-critical paths.
- No GC — predictable latency under load.
The async stack is tokio and hyper, chosen for precise control over timeouts and task limits and for a small surface area. Crypto primitives come from ring — audited and constant-time.
High-level web frameworks were rejected outright; they add abstraction and attack surface to a system whose entire job is eating hostile traffic. Python, Node, and Go were all considered and rejected — Python for runtime unpredictability, Node for the JS runtime being an attack surface, and Go for GC pauses and weaker type guarantees.
Shell is used only for install and bootstrap: OS detection, package installation, sysctl tuning, and firewall rules. Never long-running, never network-facing.
Status
Phases 0 through 6 are complete, with all crates compiling and unit tests across each phase:
| Phase | Delivered |
|---|---|
| 0 — Initialization | Repository scaffold, Rust workspace, documentation structure. |
| 1 — OS hardening | Environment detection, hardening scripts, Tor setup and validation, systemd units, config backup. |
| 2 — Core logic & trust | Five-tier trust system, HMAC-SHA256 tokens, session state machine, violation tracking and burn logic. |
| 3 — Gate system | Server-side captcha, SHA-256 proof of work, multi-step verification, rate limiting, token issuance. |
| 4 — HTTP & proxy | Token validation, reverse proxy, three routing strategies, tier-based routing, backpressure, metrics. |
| 5 — Orchestrators | Mirror lifecycle, Tor integration, multi-signal compromise detection, automatic burn and replace, three rotation strategies. |
| 6 — Node system | Dual healthy/threat modes, adaptive rate limiting, silent reclassification, anomaly detection, metrics. |
Requirements
- Linux (Ubuntu or Debian), server-grade.
- Rust toolchain.
- Tor daemon.
- Root or sudo access for installation.